APISentry Security Gateway
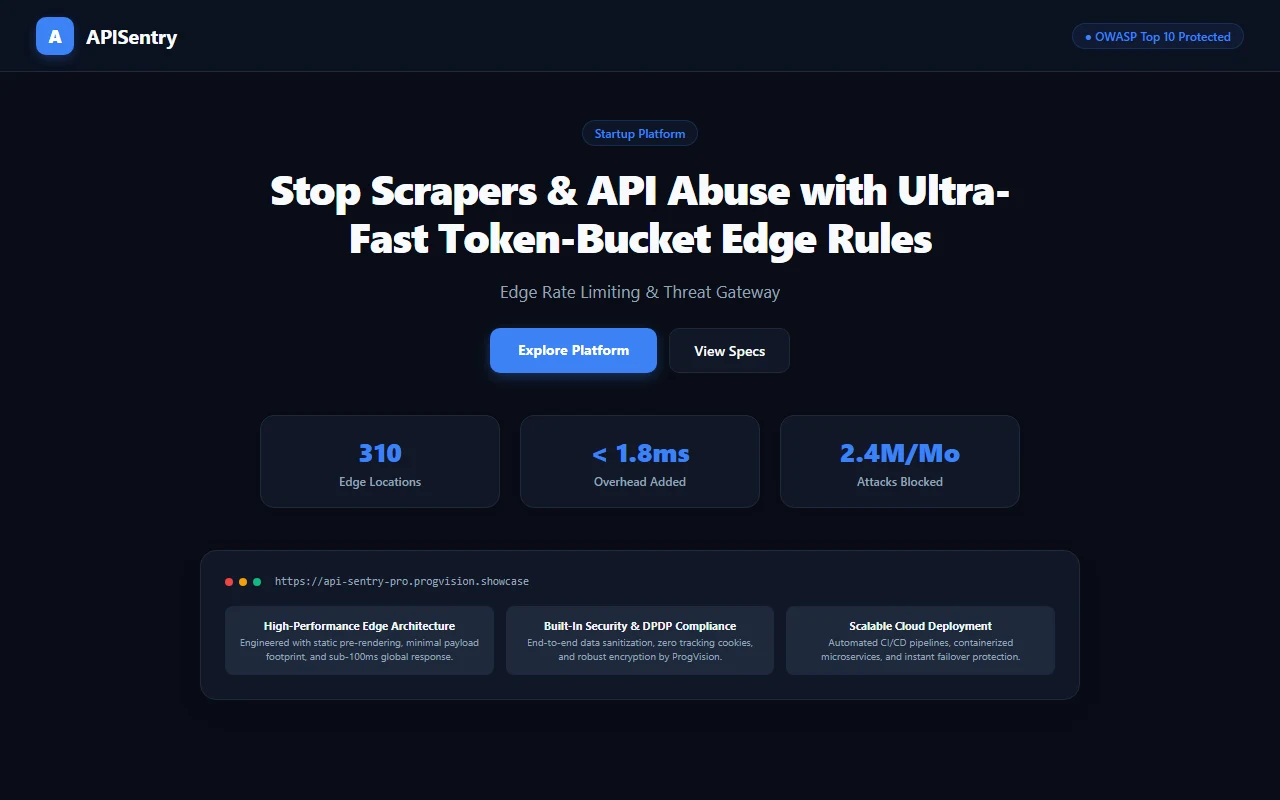
API Rate Limiting & Edge Threat Shield
APISentry Security Gateway
Startup
Hyderabad, Telangana
API Rate Limiting & Edge Threat Shield
Delivered
2 Rounds
The Challenge
Fast-growing fintech and AI startups faced crippling cloud compute bills and DDoS risks caused by aggressive scraper bots and credential-stuffing attacks hitting exposed REST APIs.
How We Started
Built in Rust and compiled to WebAssembly for execution directly on edge nodes, terminating malicious requests before they ever touch origin application servers.
Key Requirements
What We Delivered
Rust/Wasm edge threat filter module
Founder security telemetry dashboard
Automated IP ban and reputation scoring engine
Webhook alert dispatcher for security anomalies
Engineering Timeline
Wasm Edge Filter in Rust
Authored memory-safe edge inspection filter adding only 1.8ms to request time.
Token-Bucket Logic
Implemented sliding-window counter in edge key-value storage for precise quotas.
Threat Visualizer
Built dark-mode real-time threat map showing blocked attacks globally.
Penetration Stress Testing
Simulated 500,000 bot request bursts with 100% mitigation success.
Client Sign-Off & Knowledge Transfer
Completed in 2 structured revision rounds. What was handed over:
- Cloudflare Workers global route configuration
- Admin rate limit policy and threshold tuning handbook
- Threat response webhook setup guide
- Over 2.4 million malicious automated scrapers and brute-force attacks blocked per month.
- Customer origin server compute bills decreased by 42% via edge request shedding.
- Average overhead added to valid legitimate API requests remained strictly under 1.8ms.